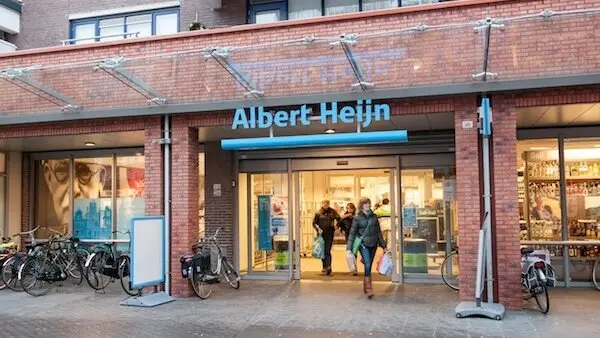
AMSTERDAM — Ahold Delhaize, the multinational retail giant and parent company of the Netherlands’ largest supermarket chain, Albert Heijn, has officially filed a formal police report regarding the sophisticated cyberattack that forced major operational systems offline more than a week ago.
The corporate announcement, made in an official statement on Monday, October 20, 2026, marks a significant shift in how the company has characterized the ongoing crisis. While Ahold Delhaize had previously referred to the severe operational disruption merely as a "cybersecurity incident," its internal investigation has now formally confirmed that the suspicious activity detected across its IT infrastructure was the direct result of the malicious actions of external actors.
The decision to escalate the matter to law enforcement follows mounting pressure from Dutch authorities. Both the national police and the public prosecution service, known by its Dutch acronym OM, publicly urged the corporate parent last week to lodge an official complaint. Under Dutch legal frameworks, a formal report from an affected entity is a crucial procedural step required to initiate and empower a comprehensive criminal investigation into digital intrusions of this scale.
While broad-caster NOS and other national media outlets reported that it remained unclear why Ahold Delhaize delayed taking this specific step for over a week after the breach first unfolded, the company has maintained steady communication with critical state bodies. Crucially, Ahold Delhaize confirmed that it fulfilled its legal obligations by notifying the National Cyber Security Centre, the dedicated cybersecurity agency operating under the Ministry of Justice and Security, within 24 hours of discovering the unauthorized access.
This swift notification aligns with a newly implemented cybersecurity law that officially entered into force on August 15 of this year. The groundbreaking legislation significantly tightens regulatory oversight and mandates immediate reporting for approximately 8,000 organizations deemed vital to the societal and economic infrastructure of the Netherlands. The scope of this vital infrastructure law spans diverse sectors critical to national stability, ranging from healthcare providers, drinking water facilities, and major financial banking institutions to essential elements of the food supply chain, including large-scale supermarket networks.
The operational crisis itself began unfolding on Sunday, October 11, when technicians and security teams at Albert Heijn detected anomalies within the corporate network and proactively switched off significant portions of the company’s IT systems to contain the threat. This defensive measure immediately paralyzed standard operations, halting online home delivery services, disrupting logistical workflows at critical distribution centers, and causing noticeable gaps and empty shelves across numerous retail locations as inventory management systems went dark.
As the days progressed, the widespread disruption rippled across the broader Ahold Delhaize family of brands. However, corporate updates on Monday offered signs of stabilization and recovery. The primary Albert Heijn website and mobile shopping application have successfully been brought back online, and company representatives announced that home delivery services are anticipated to resume by Friday, October 23. Furthermore, digital platforms belonging to related retail banners, including drugstore chain Etos and specialty drinks retailer Gall & Gall, have been successfully restored and are fully accessible to consumers once again.
Regarding the nature and potential exposure of sensitive information, Ahold Delhaize reported that ongoing forensic investigations have not uncovered any evidence indicating that confidential data belonging to customers, employees, or corporate business partners was exfiltrated or compromised during the attack. Nevertheless, the retail group exercised caution, declining to elaborate on finer technical specifics while forensic inquiries remain active, citing the necessity to protect ongoing security protocols and avoid jeopardizing the integrity of the investigation.
Security sources speaking to broadcaster NOS last week shed partial light on the international footprint of the cyberattack, revealing that digital traces and servers located in the United States, Poland, Moldova, and Turkey were actively utilized by the perpetrators during the execution of the breach. Meanwhile, industry insiders and economic analysts speaking to the prominent financial daily newspaper Financieele Dagblad estimated that the prolonged system outage and resulting commercial paralysis have been costing the retail conglomerate tens of millions of euros for each day that core systems remained offline.